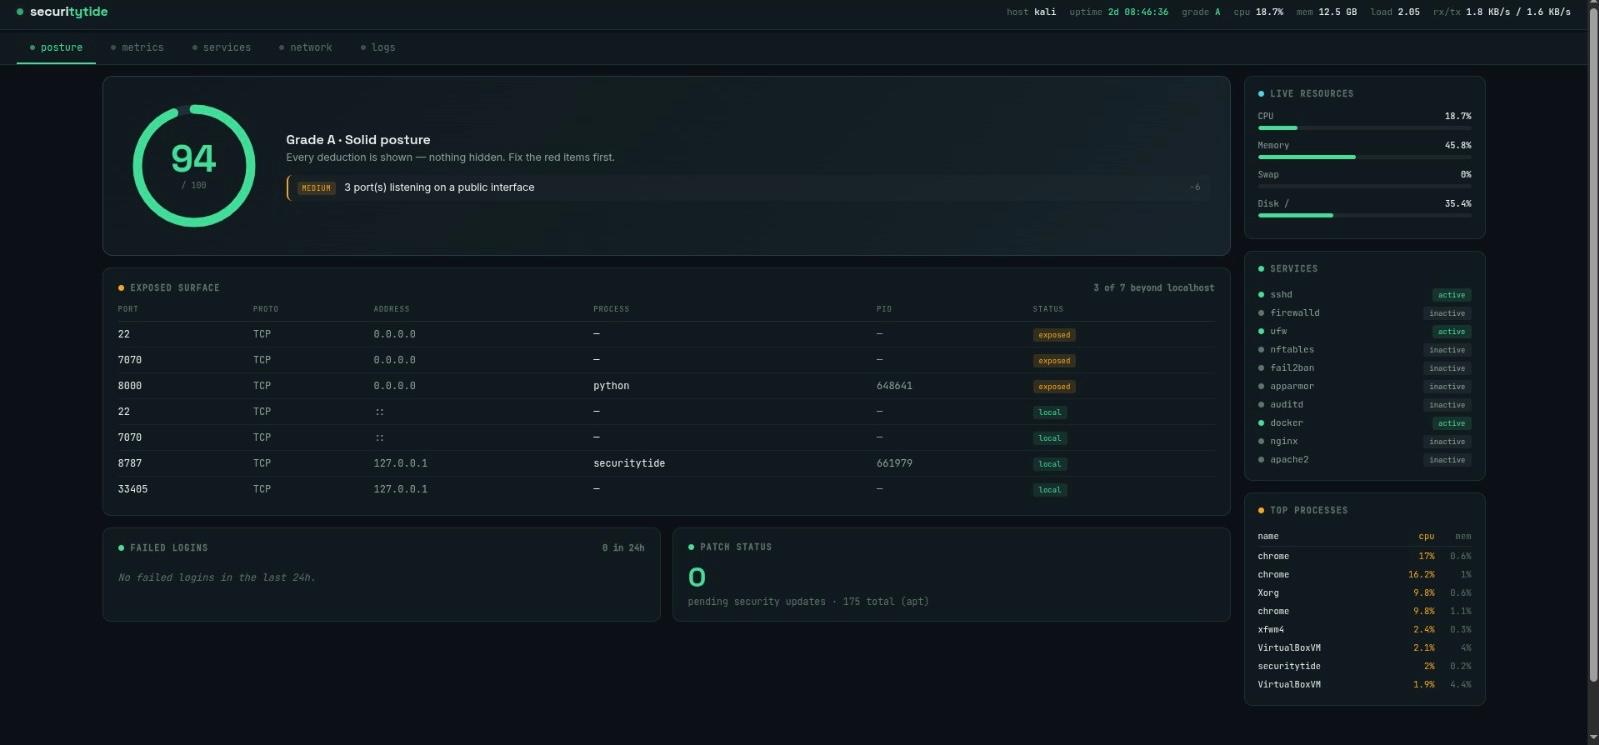
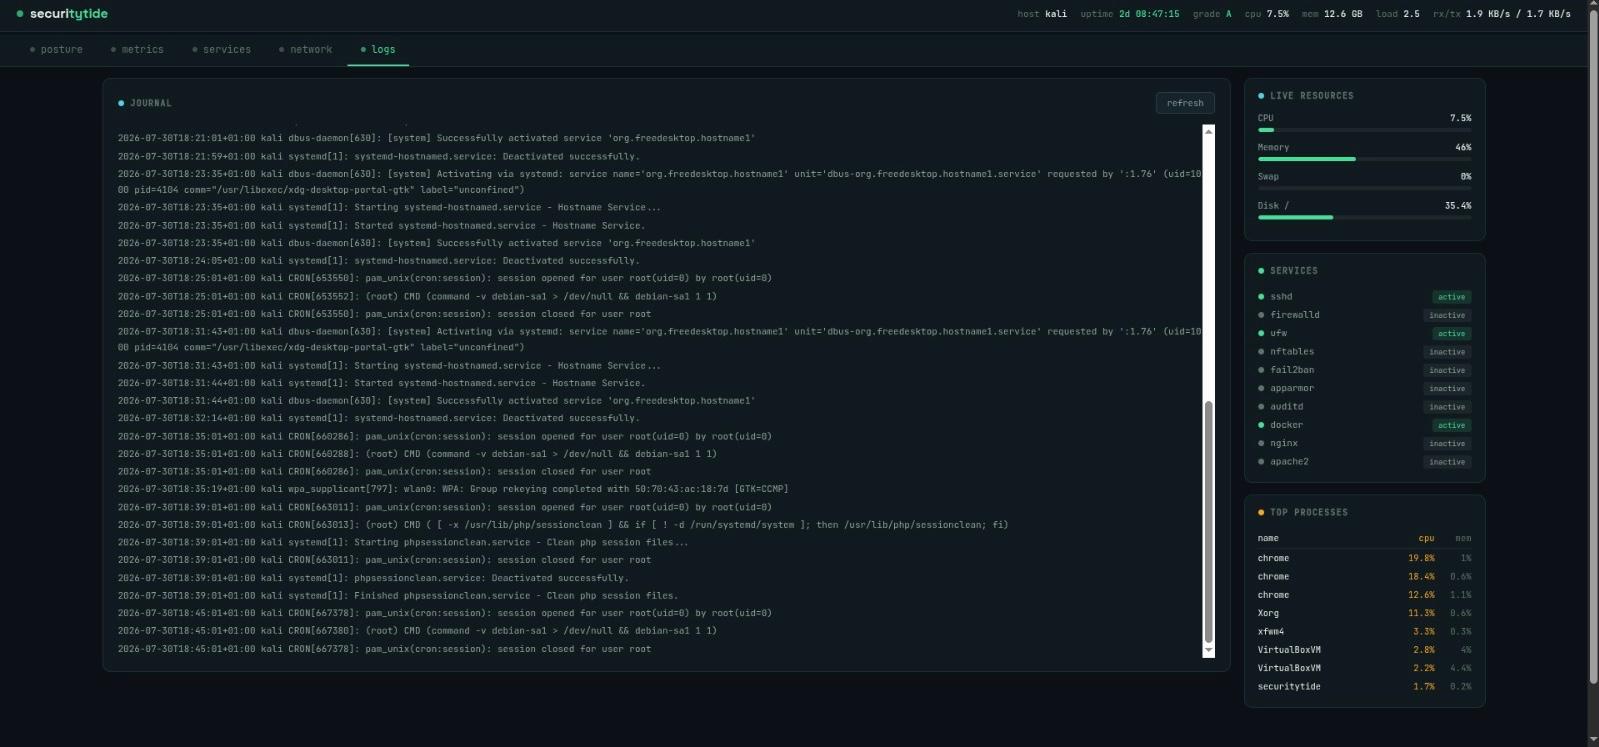
Not another CPU-and-memory dashboard. securitytide scores your host's real security posture — what's listening beyond localhost, who's failing to log in, whether your firewall is even on, and how far behind you are on patches. One command. No config, no account.
pip install securitytide-cli
securitytide
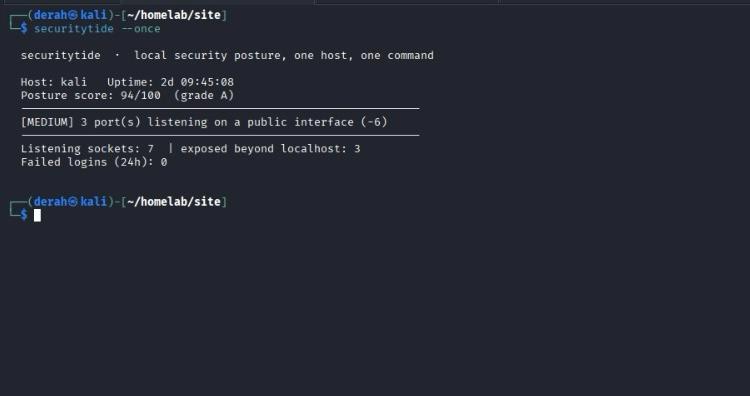
securitytide --once prints the whole report to stdout. Add --json and pipe it anywhere.Resource monitors tell you the CPU is busy. They don't tell you Redis is listening on 0.0.0.0 with no password. That's the gap this fills.
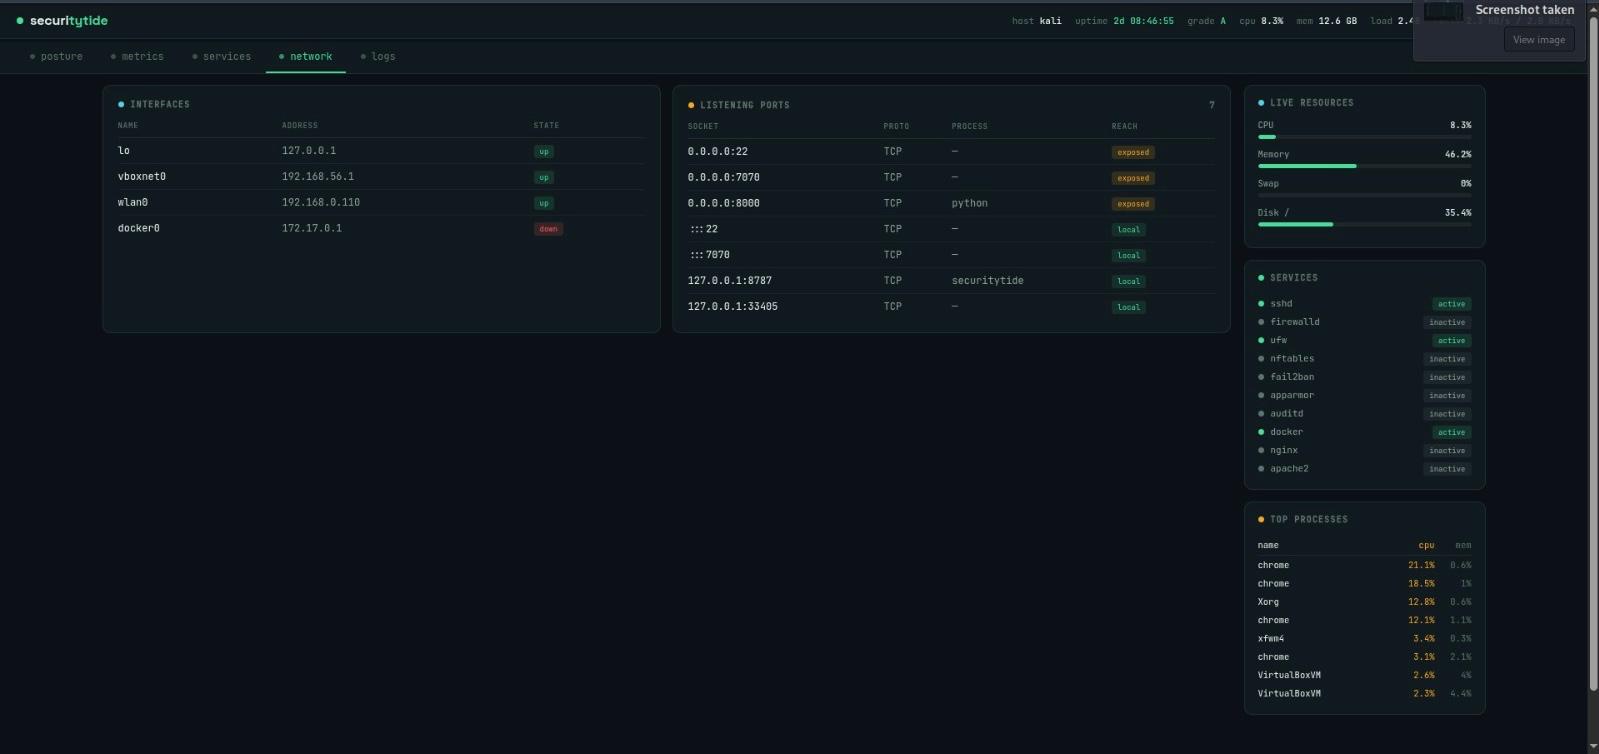
Every listening port, with anything reachable beyond localhost flagged — and known-risky services (Redis, RDP, SMB, unauthenticated Mongo, Telnet) called out by name.
Brute-force attempts over the last 24 hours, aggregated by source IP so a real attack stands out from ordinary noise.
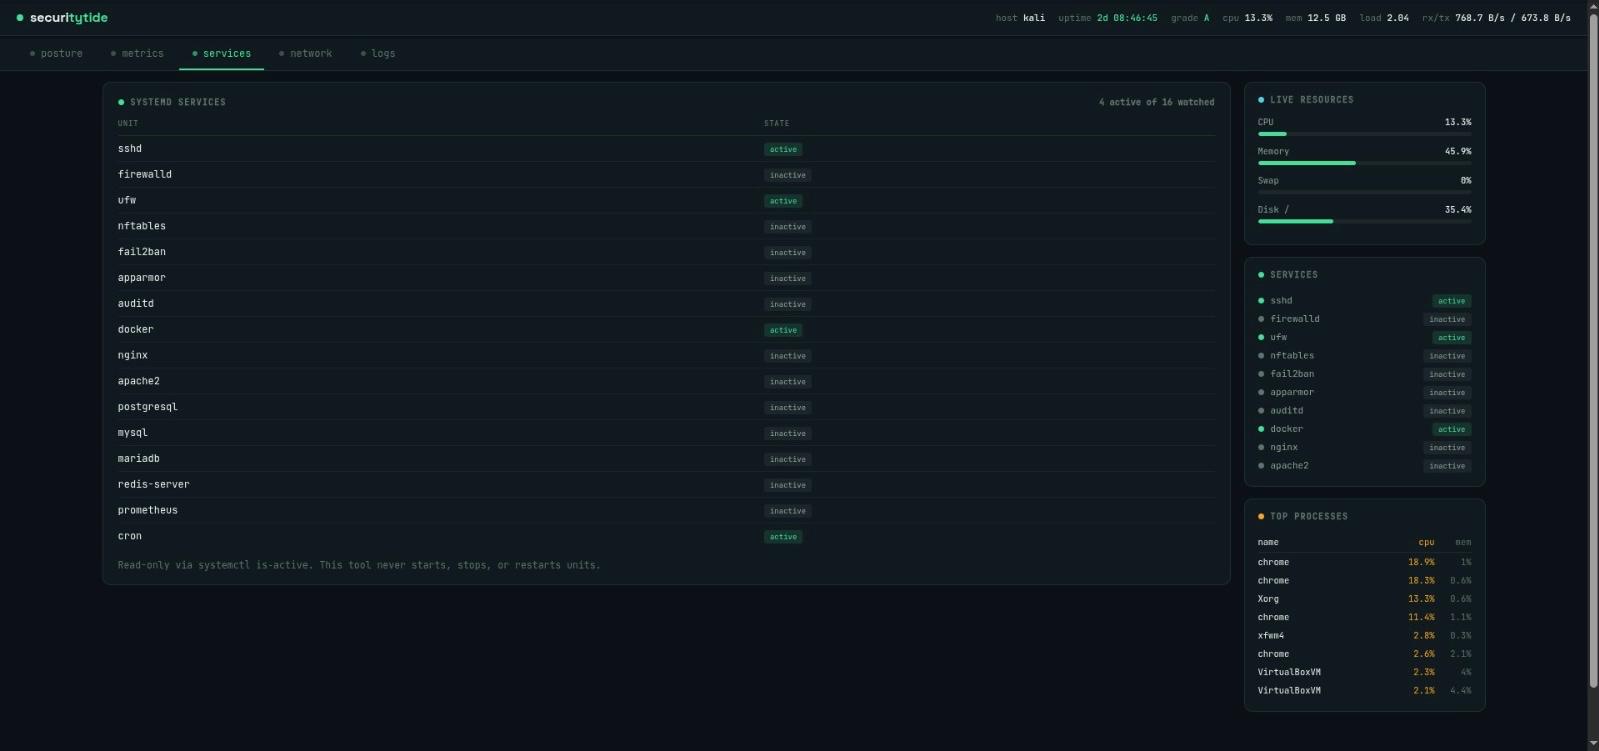
Firewall (firewalld / ufw / nftables), fail2ban, auditd, AppArmor, SSH — what's actually running versus what you assumed was running.
How many security updates you're behind, via apt or dnf. The simplest question in security, and the one most often unanswered.
A 0–100 posture grade where every deduction is itemised. You always know why you scored what you scored, and what to fix first.
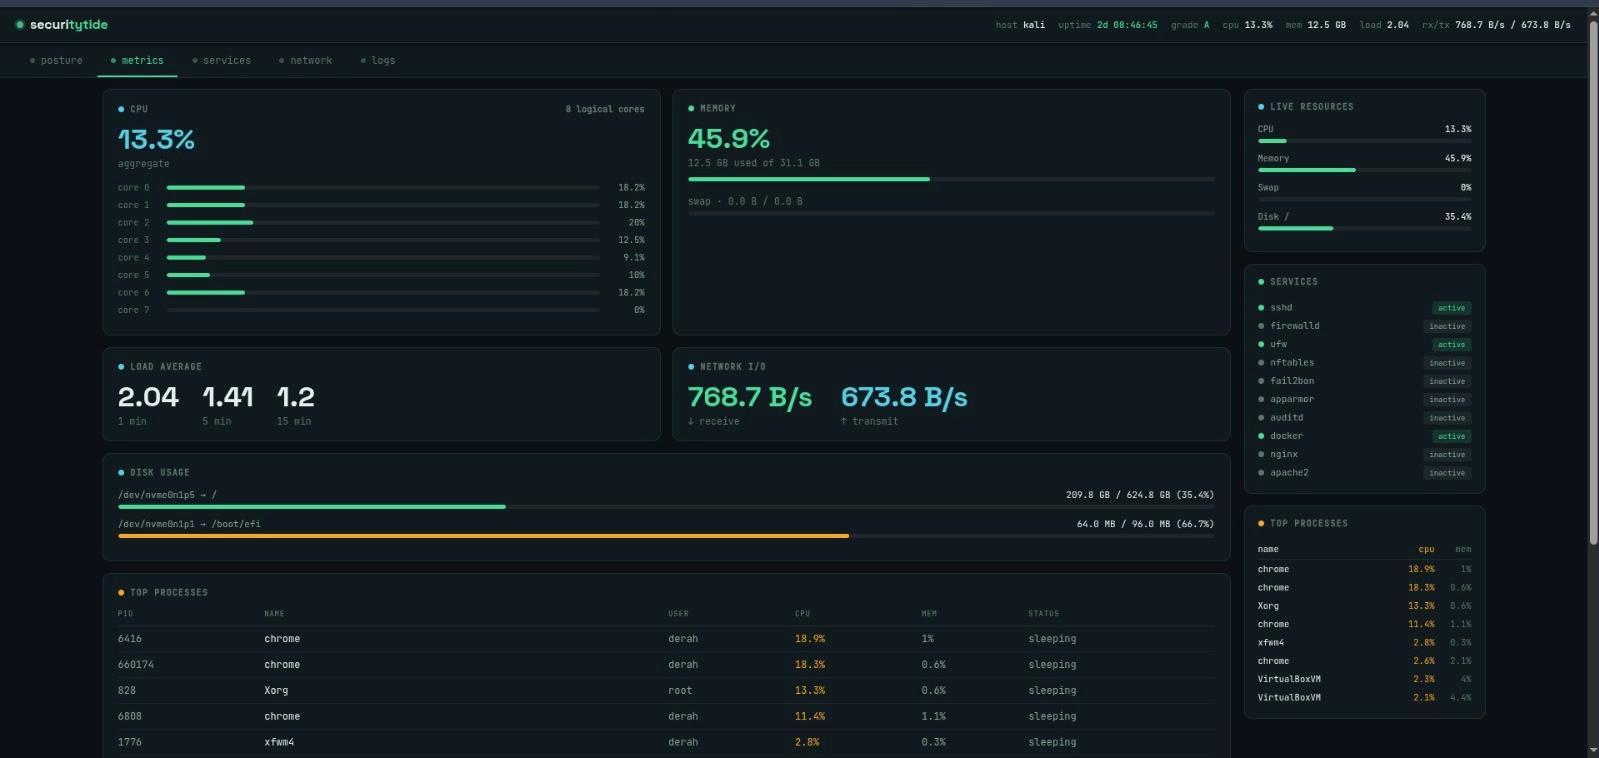
Per-core CPU, memory, load, disks, processes, interfaces, and journal logs — the ordinary monitoring you'd want anyway, in the same pane.
One pip install. No agent to register, no config file, no account to create.
From PyPI. Python 3.9 or newer, on Linux.
pip install securitytide-cli
Starts on 127.0.0.1:8787 and opens your browser.
securitytide
One-shot report, or JSON to pipe into anything.
securitytide --once securitytide --once --json
Tunnel over SSH. Don't expose the port — the dashboard maps your weak points.
ssh -L 8787:127.0.0.1:8787 you@host
This dashboard maps your host's weak points. So it's built, deliberately, to keep that map to yourself — and to be incapable of doing anything to your system even if someone did reach it.
securitytide is scoped to one machine — yours — and it isn't crippled. You only need the cloud version when one host becomes a fleet, and a fleet becomes someone's job.
| securitytidefree, open source, self-hosted | Securitytide Cloudfor fleets and teams | |
|---|---|---|
| Hosts | 1 | Unlimited |
| Posture score & findings | ✓ | ✓ fleet-wide |
| Exposed ports, failed logins, services | ✓ | ✓ |
| Metrics, processes, logs | ✓ | ✓ |
| Pending security updates | ✓ | ✓ with CVE detail |
| Full CVE cross-reference (NVD) | — | ✓ |
| AI-assisted triage & remediation | — | ✓ |
| Anomaly detection & baselining | — | ✓ |
| Alerting (Slack, email, PagerDuty) | — | ✓ |
| Compliance reporting (CIS, NIST) | — | ✓ |
| Teams, roles, audit log | — | ✓ |
| Price | Free forever | In development |
Securitytide Cloud takes the same posture engine across your whole fleet — with real CVE cross-referencing, AI-assisted triage that ranks by actual exploitability, anomaly detection, alerting, and compliance reporting. Built for the people who get paged.